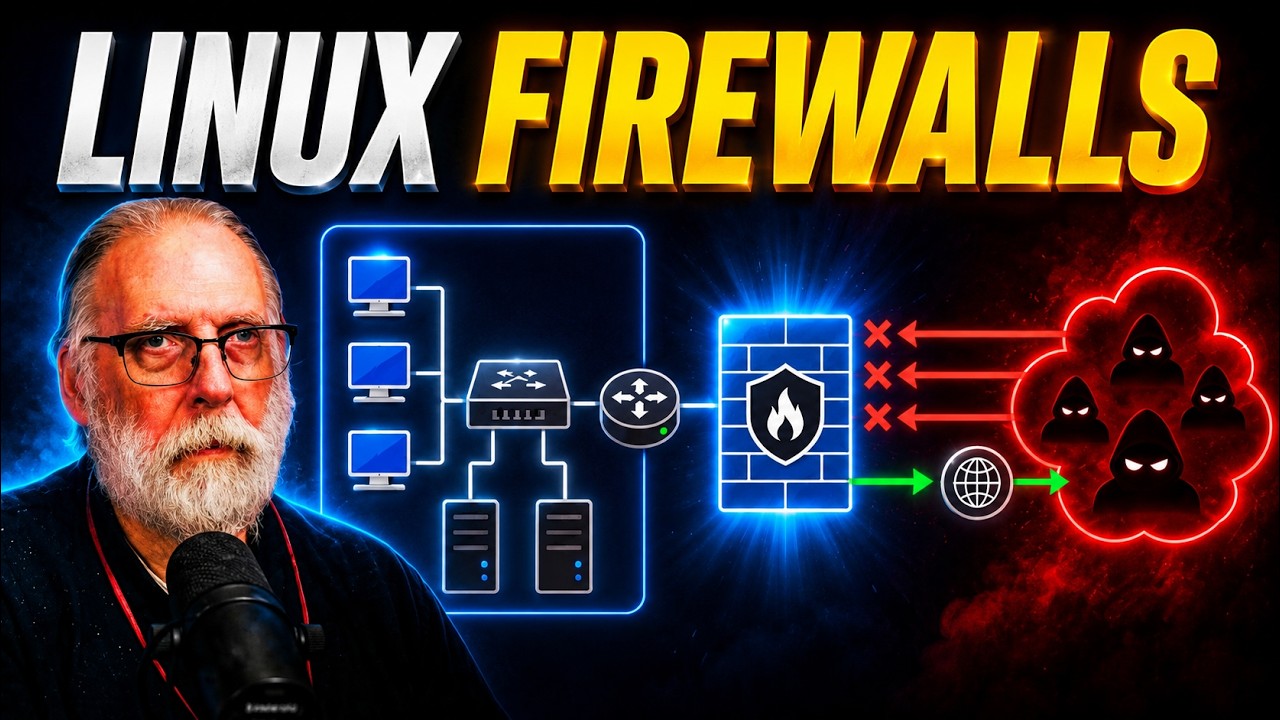
Firewalls from Scratch? You May Be Asking the Wrong Question
Most people still treat a firewall like a front door. Lock it down, keep the bad stuff out, and call it done.
That model is incomplete.
In this video I walk through why “build a firewall from scratch” is close but not the right question in 2026, and what actually matters instead:
- The dual role of a firewall (ingress + egress)
- Why outbound control belongs at the edge
- How to approach default-deny without unplugging yourself
- Why high-value hosts still need their own controls
- A practical sequence that won’t drive you crazy
I’m not going to hand you a 200-line ruleset. I’m going to show you the architecture that makes the ruleset worth writing.
**Chapters**
00:00 - Intro
00:51 - Decade 1990
01:00 - egress firewalls
01:17 - packet filter firewalls
01:51 - Stateless Firewalls
02:31 - egress filters
03:19 - Unified Threat Manament (UTM)
03:30 - Threats ni 2026
03:39 - PROMPTFLUX and PROMPTSTEEL
04:07 - Checkpoint Says
04:28 - NGFW
05:10 - Another Way
05:41 - egress
07:23 - Nexus Says my Computer isnt Genuine
09:13 - nftables + egress
09:32 - PiHole and pfBlockerNG
12:43 - Egress Monitor

DJ Ware
I would like to use this channel to give back to the community what I have learned from others. I cover a wide range of topics on computing technology from Home Server setup on a budget, Linux for general use (workstation, server and development), High P...